Google dismantles botnet secretly running on 1.3 million Android TV boxes
At a glance
Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says its screening process missed the malware due to "obfuscation techniques" employed by Shenzhen-based
- Primary source
- Ars Technica - All content — Read original article
- Published
- Topic
Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes.
Google says its screening process missed the malware due to "obfuscation techniques" employed by Shenzhen-based Videostrong Technology.
In a detailed blog post , the Threat Intelligence Group explains how the x.cpe botnet evolved quickly from a single-stage dropper into a modular three-stage malware platform that sold access to third parties.
Manufacturers must have their devices certified if they want access to Google apps and branding, a process that is supposed to catch threats like this.
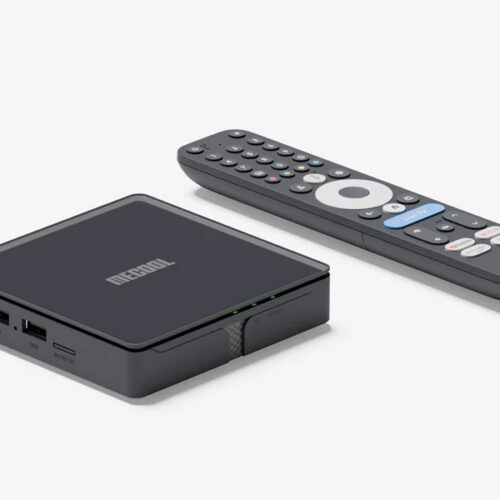
However, Videostrong's compromised boxes, mostly sold under the MECOOL brand, evaded detection by using a backdoor to remotely install the malware after the devices were set up and online.
After devices appeared online, a stub application called x.cpe or com.oemservice would phone home.
This package did not have any malicious capabilities of its own, but it had the system-level permissions necessary to install malware modules at the operator's behest. It also disabled Play Protect, which wo
This summary comes from Ars Technica - All content. Read the full article at the original source.
References
More in Google
Google says students in schools that ban AI won't have access to Search
This is another example of how closely Google Search is tied to the company's AI products.

Google is entirely disabling Search in schools that don’t want AI
Google is completely turning off Search in schools that reject its AI features, the company told The New York Times . The decision was also shared in a broader education-related…

Schools choosing to restrict AI altogether will no longer be able to access Google Search, as AI features are now integrated into the search engine.
Google takes Dreambeans to India in bid to bring AI-generated personal stories to the masses
Google's Dreambeans, its latest AI experiment, now supports 13 Indian languages.